UNLISTED REVIEW EDITIONField lab · Draft · Not in public catalog
thrivePCISite v0.43.62+20261122T201000Z · Published November 22, 2026
PAYMENT CHANGE REVIEW FIELD LAB · PACKAGE v0.1.0+20261119T221256Z
Review the change before it ships.
A practical handoff for PCI-aware change review. Gather the facts, name what remains unknown, and route impact questions to the accountable owner.
Scott’s review pass complete. This lesson remains an educational draft and does not determine scope, significance, compliance, applicability, or assessment results. The route is noindex and unlisted, but is not private or access-controlled.
No audio, video, or timed captions are included. The narration is an owner-recording script. Slide previews below are images; download the PPTX to inspect and record from the editable deck.
FICTIONAL PRACTICE
Harbor Learning adds subscriptions.
A proposal names a hosted payment service. A provider says card details are tokenized. The current flow diagram still shows one-time payments. The lesson asks what to verify and who should review impact.
The fictional scenario contains no client data and leaves the facts incomplete by design.
SLIDE-BY-SLIDE REVIEW
Eight editable slides
Each preview links to the slide text and owner narration. The editable deck remains the recording source.
SLIDE 01 · change-review-01
Review the change before it ships
Describe what is changing
Gather facts that can be checked
Route impact questions to the right owner
Read owner narration script
Welcome. In this short field lab, we will practice a useful handoff when a payment-related change is proposed. We will not decide whether a system is in scope or whether a requirement applies. Instead, we will make the change understandable: what is different, which facts need confirmation, what records may need attention, and who should evaluate the impact. Our example is fictional. Use the process to improve questions and coordination, then use the actual environment, current PCI DSS text, and the responsible parties for any real determination.
SLIDE 02 · change-review-02
A change is a signal to look closer
Capture the before and proposed after
Separate confirmed facts from assumptions
Route impact and scope questions to the accountable reviewer
Preparation helps the review. It does not make the determination.
Read owner narration script
A change ticket is an invitation to ask what else may need review. Start with a clear description of the current state and the proposed state. Mark what is confirmed, what came from a proposal, and what is still unknown. The goal is not to label the change as significant or insignificant from a title alone. PCI DSS Requirement 12.5.2 addresses documenting and confirming scope at least every twelve months and upon significant change to the in-scope environment. Whether a particular change is significant depends on the environment and the applicable requirements. This field lab gives you a way to prepare the facts for the people responsible for that evaluation.
SLIDE 03 · change-review-03
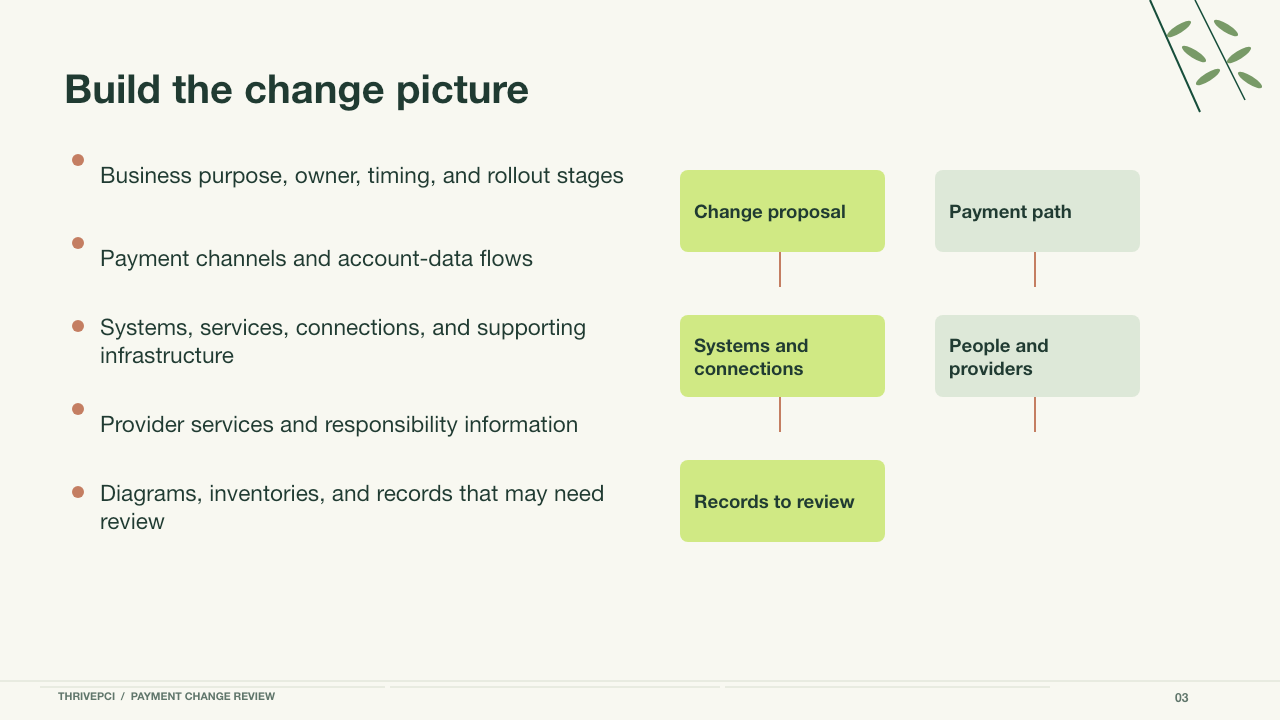
Build the change picture
Business purpose, owner, timing, and rollout stages
Payment channels and account-data flows
Systems, services, connections, and supporting infrastructure
Provider services and responsibility information
Diagrams, inventories, and records that may need review
Read owner narration script
Gather the change facts before forming a view. What business capability is being introduced? Which channels are affected? How is account data entered, transmitted, stored, or otherwise handled in the proposed design? Which systems and connections are new or changed? Which provider service is involved, and what does the service actually do? What supporting infrastructure or responsibility information may need attention? Requirement 12.5.2 lists minimum elements for scope validation, including payment data flows and channels, account-data locations, system components, segmentation controls, and third-party connections. This is a preparation conversation, not a replacement for the full requirement or its testing procedures. Use current source records and note uncertainty explicitly.
SLIDE 04 · change-review-04
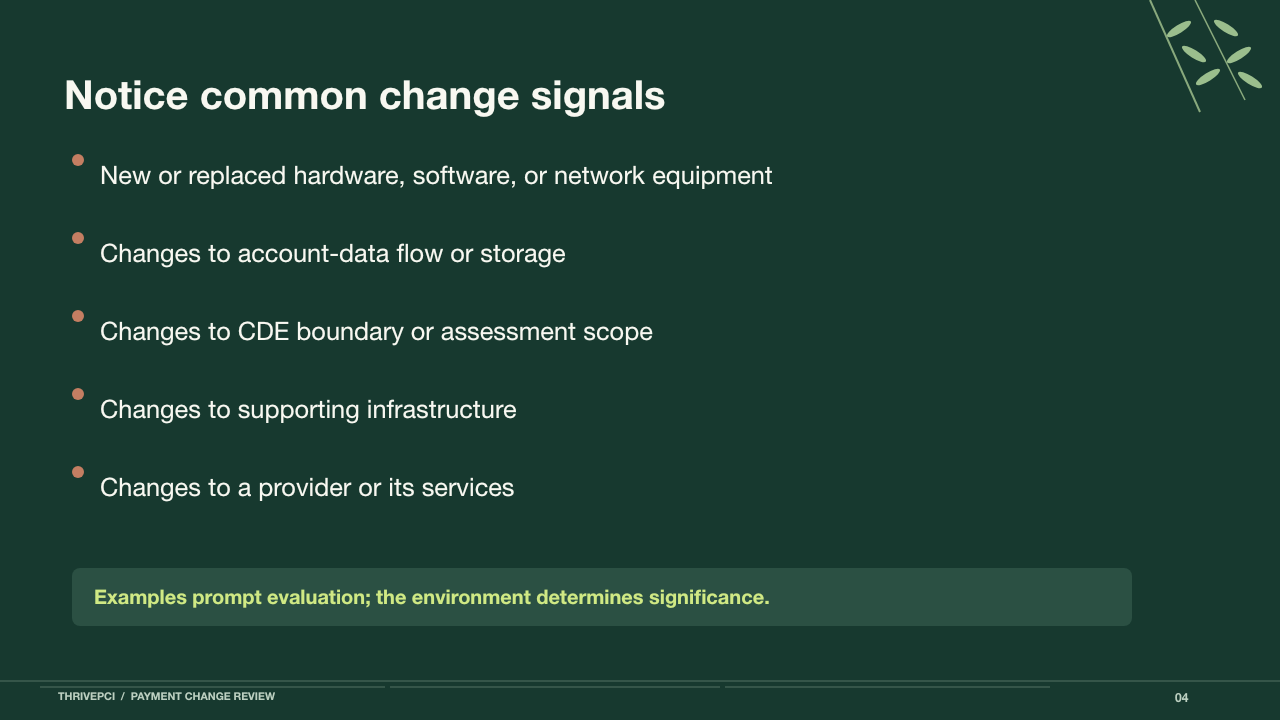
Notice common change signals
New or replaced hardware, software, or network equipment
Changes to account-data flow or storage
Changes to CDE boundary or assessment scope
Changes to supporting infrastructure
Changes to a provider or its services
Examples prompt evaluation; the environment determines significance.
Read owner narration script
PCI SSC FAQ 1317 describes examples included in the significant-change definition: new or replaced hardware, software, or networking equipment in the CDE; changes in the flow or storage of account data; boundary or assessment-scope changes; changes to supporting infrastructure; and changes to relevant third-party providers or services. The FAQ also explains that significance depends on the configuration of the particular environment and that the listed activities have potential impact and must be considered in context. Treat these as signals to investigate. Do not use a checklist result to declare that a change is or is not significant. Record which facts support the review and who is responsible for the conclusion.
SLIDE 05 · change-review-05
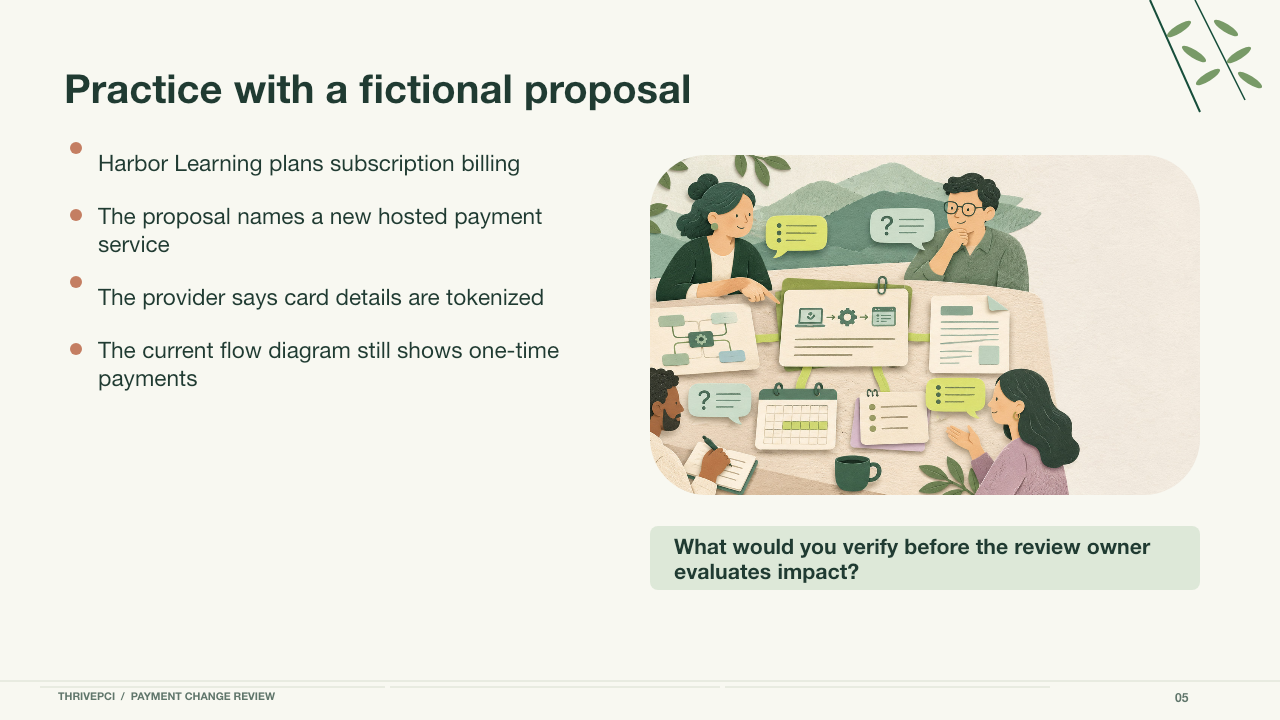
Practice with a fictional proposal
Harbor Learning plans subscription billing
The proposal names a new hosted payment service
The provider says card details are tokenized
The current flow diagram still shows one-time payments
Practice prompt: What would you verify before the review owner evaluates impact?
Read owner narration script
Harbor Learning plans to add subscription billing. A proposal names a new hosted payment service. A provider contact says card details are tokenized, but the statement is not yet tied to Harbor’s exact configuration. The current flow diagram only shows one-time payments. What should the team do next? It should verify the consumed service, payment stages and channels, data entry and transmission, any storage, system connections, and the evidence behind the provider statement. It should identify the diagram owner and the person responsible for the impact review. The team should not declare the service out of scope because the page is hosted, or in scope because a provider is named. The facts are incomplete; the handoff should make that visible.
SLIDE 06 · change-review-06
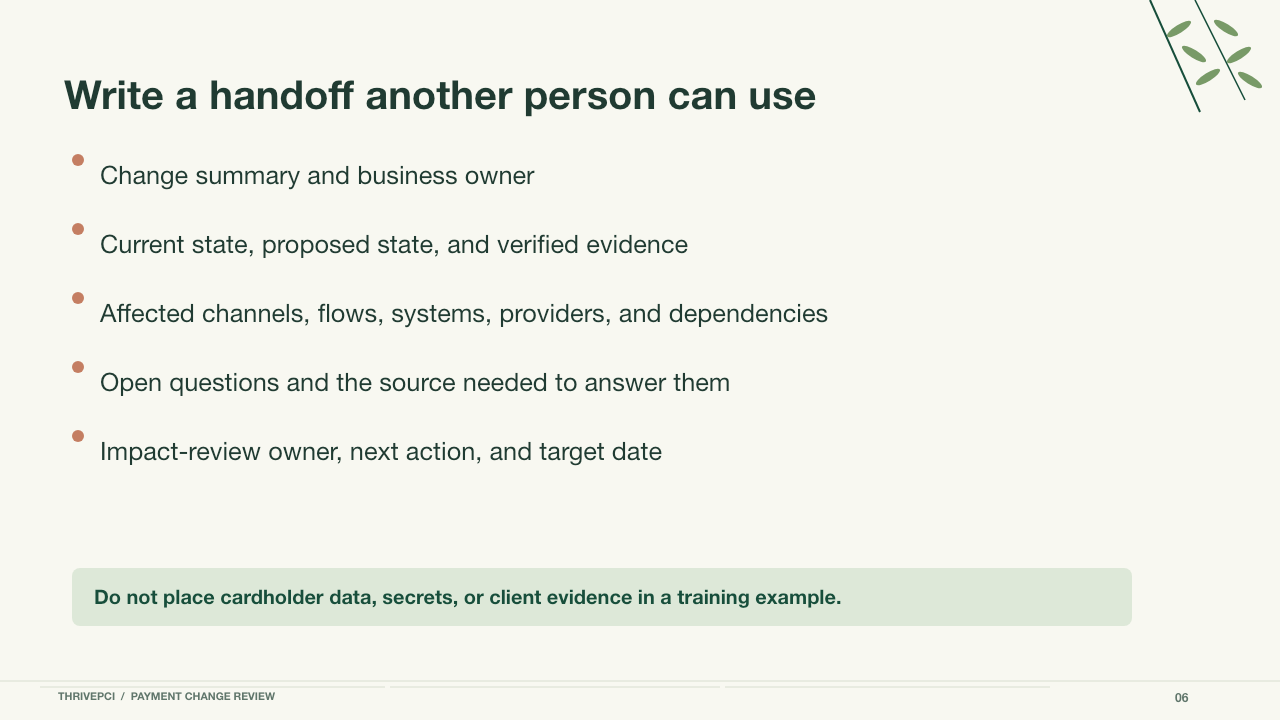
Write a handoff another person can use
Change summary and business owner
Current state, proposed state, and verified evidence
Affected channels, flows, systems, providers, and dependencies
Open questions and the source needed to answer them
Impact-review owner, next action, and target date
Do not place cardholder data, secrets, or client evidence in a training example.
Read owner narration script
A useful handoff is short enough to read and specific enough to act on. Name the change, the business owner, and the proposed timing. Describe the current and proposed payment flow using source records rather than assumptions. List systems, services, providers, connections, and supporting dependencies that may be affected. For every unknown, name the question and the person or record that can answer it. Identify the accountable reviewer and the next action. A tracker can help coordinate this work; it is not evidence that the review is complete. Keep sensitive data out of shared training materials and public channels. For a real project, follow the organization’s approved data-handling practices.
SLIDE 07 · change-review-07
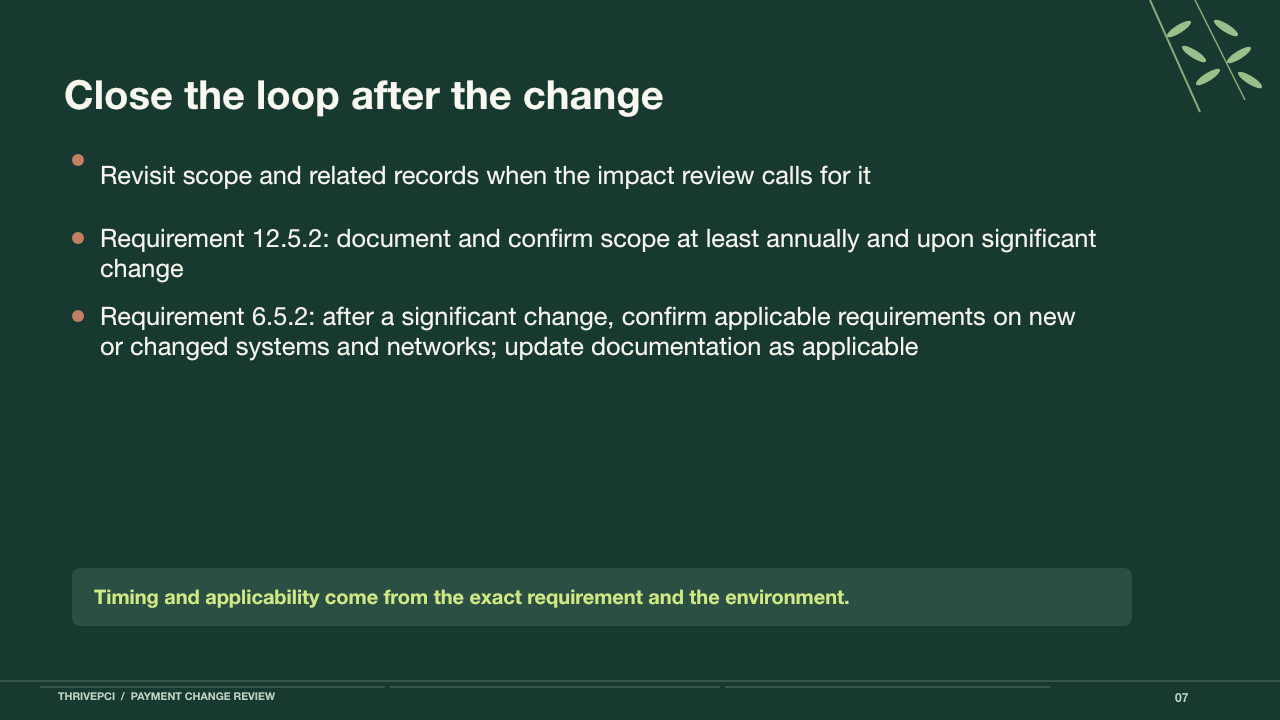
Close the loop after the change
Revisit scope and related records when the impact review calls for it
Requirement 12.5.2: document and confirm scope at least annually and upon significant change
Requirement 6.5.2: after a significant change, confirm applicable requirements on new or changed systems and networks; update documentation as applicable
Timing and applicability come from the exact requirement and the environment.
Read owner narration script
The review should end with an owned next step, not an untracked conversation. Requirement 12.5.2 states that scope is documented and confirmed at least once every twelve months and upon significant change to the in-scope environment. Requirement 6.5.2 separately addresses completion of a significant change: applicable requirements are confirmed to be in place on new or changed systems and networks, and documentation is updated as applicable. Do not collapse these provisions into one blanket workflow or assume every change triggers identical work. Follow the exact applicable requirements, their notes, the system facts, and the assessment instructions. Record what the authorized reviewer concluded and which follow-up remains open.
SLIDE 08 · change-review-08
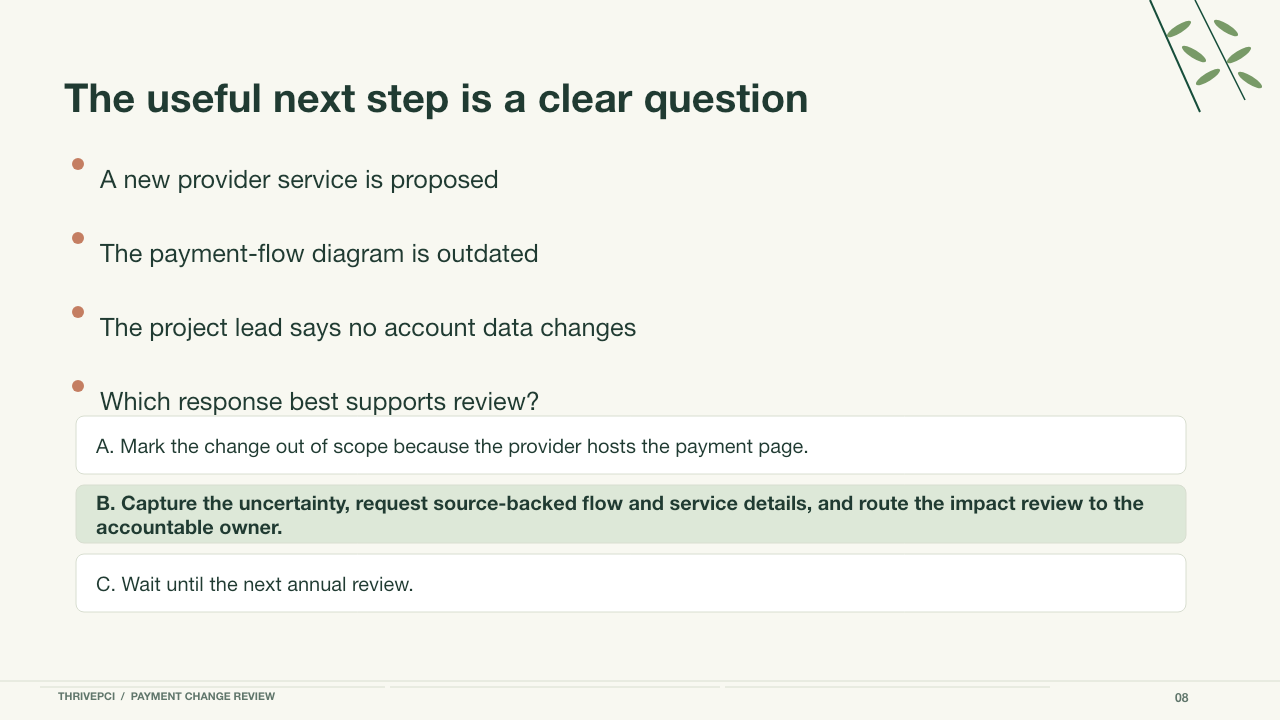
The useful next step is a clear question
A new provider service is proposed
The payment-flow diagram is outdated
The project lead says no account data changes
Which response best supports review?
A. Mark the change out of scope because the provider hosts the payment page.
B. Capture the uncertainty, request source-backed flow and service details, and route the impact review to the accountable owner.
C. Wait until the next annual review.
Reviewer answer and rationale
Answer: B. The facts are incomplete. Gather and correlate source information, then let the responsible reviewer evaluate impact. The training aid does not determine scope or significance.
Read owner narration script
Choose the response that best supports a responsible review. A is not supported: hosting alone does not establish the result. C delays a question that may need attention as part of the proposed change. B makes the information gap visible, asks for source-backed details, and assigns the impact review to the accountable owner. The answer is not a scope conclusion; it is a better next step. Take one proposed payment change from your own environment and write a three-line handoff: what is changing, what facts remain unverified, and who owns the next review. Keep the system’s actual facts and the current PCI DSS source in view. This lesson is a preparation aid, not a compliance determination.
SOURCE REVIEW
Technical sources to verify
PCI DSS v4.0.1 Requirements and Testing Procedures, Requirements 12.5.2 and 6.5.2. PCI SSC Document Library.
PCI SSC FAQ 1317 for significant-change examples and context.
Confirm exact wording, timing, applicability, and source currency against the supplied authoritative DOCX and current PCI SSC materials. Record any correction before narration.
Technical review remains open. The slide deck is editable and passed structural/layout validation. That validation does not establish PCI content approval or native PowerPoint playback.